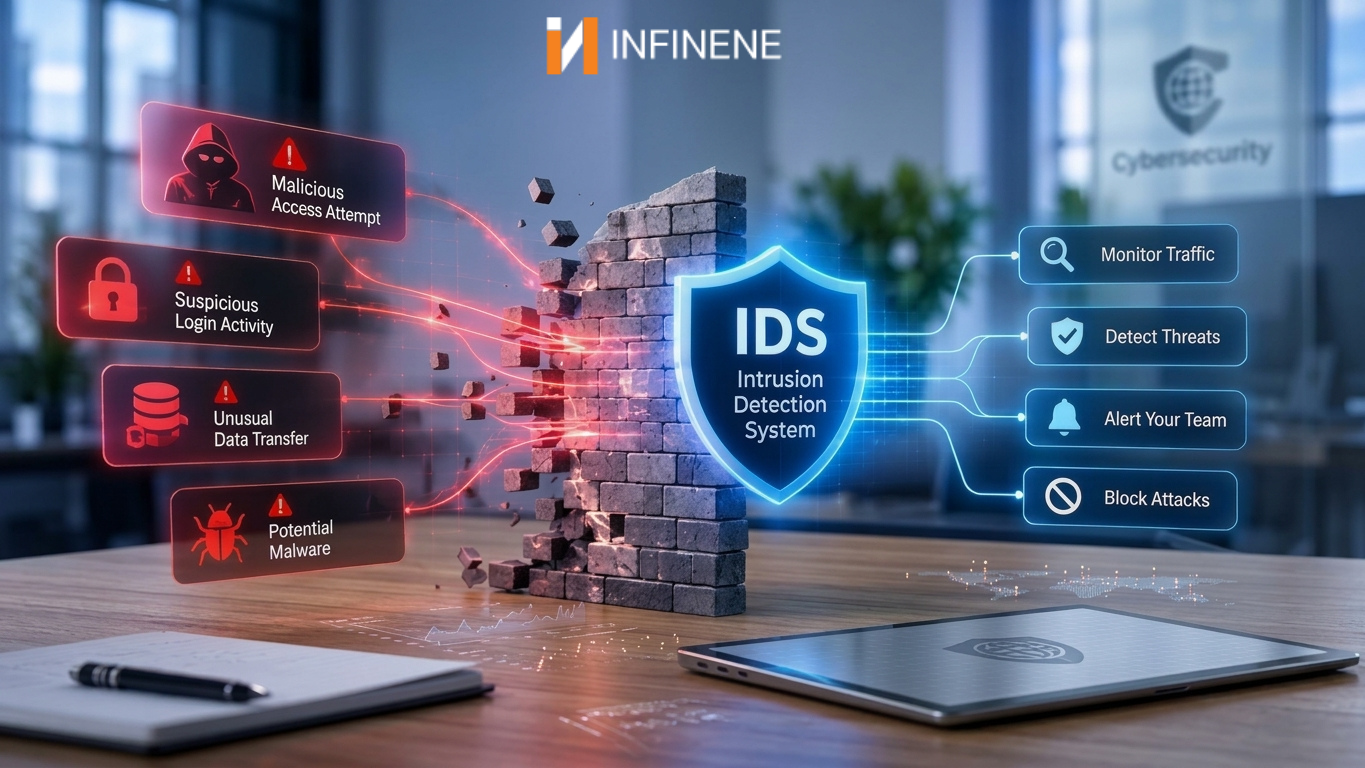
Ask a business owner where the company network begins and ends, and you'll usually get a pause. There are office computers, sure. There are also laptops on kitchen tables, a handful of cloud apps nobody remembers signing up for, a customer portal, and half the team's phones on the guest WiFi. Every one of those is a door. Attackers only need one that's unlocked.
The hard part is that early trouble rarely looks like trouble. Somebody tries a few wrong passwords. A laptop starts talking to a server in a country you've never done business in. A file transfer kicks off at 3 a.m. Any of it could be harmless. Any of it could be the first move in a breach. Unauthorized access and odd network traffic are usually the first clues, and you can't respond to what you never saw. This is where intrusion detection systems earn their place. They keep an eye on activity across your network and raise a hand when something looks wrong. Your team gets an alert and decides what to do about it. A smoke detector works the same way. It can't put the fire out, but you'd much rather have one.
In this guide we'll go through what is IDS, what intrusion detection can catch, what it tends to miss, and how to make it work harder for you. If you'd like the wider view first, our post on how our cyber security services keep you safe covers the day to day side of protecting a business.
An Intrusion Detection System, also known as IDS, monitors the network or system for an attack or a suspicious activity. When it finds a potential threat or a violation, it documents the event. The system then issues a warning. It is up to the person or another system to determine the next course of action. Notice what's missing from that definition. Blocking. A basic IDS reports. It doesn't step in.
What does it actually watch? That depends on how it's set up. Some versions read the network packets flying past. Others read server logs. Others keep tabs on file changes and logins on a single machine. Every tool operates by either checking an event against a collection of rules, or by establishing what normal looks like, and making a decision as to whether that event requires attention. If it does, you are notified. A good alert will let you know what occurred, the time, the system concerned, and why the tool rejected it.
Let's illustrate with an example. An employee's account makes forty failed log-in attempts in under five minutes. The attempts occur from an offshore IP address. There is no such thing as super-fast, long-distance teleportation, so this isn't normal. The system identifies password guessing as a possible scenario. Your security team locks that account and resets the password. An attacker, having exhausted their guessing possibilities, takes their chances elsewhere. With no alert, the guess-attempts could have carried on through the rest of the weekend.
The mechanism of intrusion detection is simpler to break down if it's considered in sequential steps. These steps form a cyclical process and there are five steps.
The first step is data collection. This involves capturing network packets or capturing activity logs of an individual computer or host. For the most part, the network intrusion detection system has sensors to capture data, but in other instances small software agents collect the necessary data on laptops or servers.
Step two involves the analysis of the collected data. During the analysis step, the system reviews data against known attacks. Additionally, the system looks at normal patterns for a business.
Next, we look for any patterns in this. This could be anything from an attack being launched against a known vulnerability, a port scan or if an employee has violated your network policy by using a prohibited protocol.
When the system identifies any suspicious patterns it will create an alert. It will also include information about the incident including date, time and which rule/signature was triggered.
Your security team or one of your security tools will then review the alert and take the required actions to make sure your network is secure.
That last step is where a lot of companies fall down. An alert nobody reads is just a notification. Plenty of real breaches have started with a warning that nobody looked at. The people and process behind your intrusion detection systems matter as much as the software does.
Detection itself comes in two main flavors. Signature based detection compares activity to a library of known attack patterns, a bit like checking fingerprints. It's quick and accurate on threats it already knows. Brand new threats walk right past it.
Anomaly based detection works the other way around. It learns what normal looks like on your network. Then it flags whatever strays too far from it. That helps with odd or unfamiliar behavior. The downside is noise. Expect more false alarms, especially in the first few weeks. Most modern tools mix both approaches.
Intrusion detection can be implemented in a number of ways, most businesses will include a mixture of different types of intrusion detection. Below outlines the primary types of intrusion detection systems.
This type of system detects intrusions by monitoring the network. Sensors are typically placed close to the firewall or on the edge of the network. They can also be located between internal segments. This means that one sensor can monitor traffic from many devices making it an efficient starting point.
NIDS are good at detecting scanning, exploitation and unusual communication patterns. It has a blind spot, though. It only sees what passes by its sensor. Encrypted traffic, or traffic that takes a route around the sensor, goes unseen. Open source tools like Snort, Suricata, and Zeek are common here, and many paid products build on the same ideas.
This type of monitoring is performed on a central device such as a server or a workstation. The monitoring looks at changes to log files, files, processes and logins.
That inside view catches things the network can't. If malware quietly edits a system file, a host based tool can notice. The cost is upkeep. You have to install and maintain software on every device you want covered, and with a few hundred machines that get old quickly.
Either method can run inside either type of system. Signature rules are dependable for known threats and need little setup. Anomalies can be detected using these models, however there is a learning phase and they require frequent adjustments. To get the best results a combination of these methods should be used and both adjusted to suit the business. This adjustment rarely stops.
Repeated failed logins are the classic sign. Logins at odd hours or from places your staff never work are another. An IDS can flag brute force attacks, password spraying, and stolen credentials being tried one after another. Catch this early and the attacker never gets a foothold.
Before launching any attacks, attackers will scan for open ports, active devices and old software. This creates a pattern which can easily be detected by an IDS. It's a heads up that someone is testing your doors. If you ignore it, a real attempt often comes next.
Most malware will need to communicate with the outside world, this could be to download more tools from a command server or transmit data. An IDS can detect this communication especially if it is to a known bad address. Whilst it may not detect the actual malware file, it can detect what it is doing on your network and this is often enough to take action.
Attackers love known software flaws. They send specially built requests that trigger a bug and open a way in. Signature rules catch a lot of these. It can also identify any unusual usage of protocols such as strange commands hidden within normal web traffic.
Sometimes the threat is already inside. A compromised laptop starts scanning its neighbors. An employee copies a huge folder to a system nobody recognizes. Traffic moving sideways between internal devices is a strong sign that an attacker is spreading out. Sensors placed inside the network intrusion detection system, and not only at the edge, are what catch it.
Now for the part people tend to skip. Intrusion detection systems are useful, but they aren't a shield. Intrusion detection and prevention systems are a single element of a wider defense strategy, as discussed in the NIST guide to intrusion detection and prevention systems. So it is wise to be aware of some limitations.
Most web traffic is encrypted these days. This is a good thing for privacy but makes things difficult for sensors. The IDS will have to make assumptions based on the size, time and where the data is going. Attackers know this so will use encryption to hide them. Some companies will decrypt at certain points which does work but can be expensive and adds complexity.
A zero day attack uses a flaw nobody has patched, or even documented, yet. Signature rules have nothing to match against, so they stay silent. Anomaly detection might catch the strange behavior. It might not. This is the biggest reason an IDS should never be your only line of defense.
A false positive is an alert about something harmless. A false negative is a real attack that nobody noticed. Both cause trouble.
Too many false positives wear a team down. People start skimming alerts, and that's exactly when the real one slips through. Too many false negatives give you a false sense of safety. Tuning helps a lot. It won't get either number to zero.
IDS tools only see what they are pointing at. If you don’t get your sensor placement right you can miss whole areas. Often cloud workloads, remote employees and new offices aren’t covered. Rules can become outdated. Many companies deploy the tool and don’t look at it again. They get a warm feeling and leave it there, but these blind spots will creep up on them.
A standard IDS detects and alerts. That's it. If nobody reads the alert quickly, the attacker keeps going. An alert at 2 a.m. doesn't help much if the dashboard gets checked at 9. Round the clock monitoring matters here, and so does having a named person responsible for every alert.
An IDS detects and alerts. It sits off to the side, watches a copy of the traffic, and tells you what it saw. An intrusion prevention system, or IPS, sits directly in the path of the traffic. It can spot a threat and block it right then. Here is a basic IDS/IPS comparison.
So IDS/IPS, which is better? Neither, really. It's a trade between control and risk. An IPS reacts fast, but one overly aggressive rule can block legitimate traffic. Imagine your sales team suddenly can't reach the customer portal because a rule got twitchy. That's a real cost.Intrusion Detection Systems are a more secure option to use, however requires human intervention which is slower than using software.
Smaller companies with a small IT department tend to be more prevention oriented. This is because it works automatically. Larger ones that want deep visibility usually want detection as well. A lot of businesses end up with both, and that's usually the right call.
For most businesses, the honest answer is whenever you can afford to. An Intrusion Detection/Prevention system is concerned with two different aspects of the problem. Prevention gives you immediate protection against known malicious activity. Detection provides you with the bigger picture. It will tell you what was missed, what looks suspicious and will give you something to take a closer look at. With just prevention you would not know what it had missed. If you only have detection, you'll find out about attacks after they happen.
A combined setup makes the most sense in a few situations. You handle sensitive customer data. You have compliance rules to meet. Your network is growing and the number of remote users goes up every month. Or you've already seen something suspicious and want better coverage.
Many modern products bundle both functions. To do this sensibly, run the rules in detection mode (to fine tune) and then move to blocking certain rules once you are confident of what they are picking up. That way you don't accidentally cut off something important on day one.
Buying the tool is the easy bit. Getting real value out of intrusion detection systems takes ongoing effort. These habits make the biggest difference.
Start with where the sensors go. Map your network before you place anything. Cover the edge, your critical servers, and the lines between internal zones. Don't forget cloud environments and remote access points. A sensor in the wrong place is just an expensive box.
Next, tune the rules. A default configuration is unlikely to be suitable. Turn off any rules you aren’t using and ensure thresholds are set so you don’t get alerted to regular activity. Ensure you are using up to date signatures, with new threats constantly appearing it is easy for your rule set to become outdated quickly.
Mix your detection methods. Signature based and anomaly based detection work better as a pair. Add host based tools on your most important systems, like the ones holding customer records or payment data.
Think about who's watching, too. Incidents can occur at any time. A managed service provider can monitor your alerts 24/7 if you cannot have someone on your team working late hours.
Link your IDS to your tools. When its alerts sit next to firewall logs and endpoint data, patterns get much easier to see. One odd login means very little. That same login followed by a strange file transfer means a lot.
Create and execute an incident response plan. Determine who will triage alerts, who has the authority to isolate and what contact details you have. Regularly test your response and look for new blind spots when changes are made to the network.
IDS (Intrusion Detection System) are security tools which monitor activity on your networks/systems to detect any malicious behaviour. If any suspicious activity is found it will alert you and your security team. It will not stop threats by default but will provide visibility.
IDS are threat detection tools which alert you to threats. IPS are threat blocking tools. One is passive whilst the other is active in the traffic flow. Many businesses will have both.
Not at all. It will fail to detect zero day attacks, threats within encrypted data and anything not in its sight. Also there will be false positives. It should be used as part of multiple layers.
No. A network IDS will only give visibility. However, without firewalls, endpoint protection, frequent patching, staff training and response plans, it won’t help you overcome poor password security, patch or prevent an attack.
Yes, often. Whilst larger companies are definitely targeted small businesses are heavily targeted due to their lack of security. You don’t really need enterprise level tools to protect your business, using a simple but well managed tool or service will provide good security without needing a large team.
Intrusion detection systems allow visibility into what is going on across your network. They can identify any unauthorised access, scanning, malicious activity, exploitation attempts or unusual activity on the network.
However, they do have their limitations. If the traffic on the network is encrypted, new attacks are used or there are too many false positives then they can be bypassed. As alerts themselves do not prevent anything, intrusion detection is best used alongside prevention tools, constant monitoring and a clear incident response plan.
If you are unsure what your network is like, Infinene can help you. We can help you understand what you need for your IT security and monitoring. We will look at what you have currently and identify any gaps. We will then create a plan to fit your business. If you'd rather work with a local team, our guide to finding IT support that actually works shows what to look for. Get in touch with Infinene to get started.
Marketing Fundamentals: A Practical Guide to Growing Your Business
Growth Navigate Startup Tools: Building the Right Technology Stack for Growth
Managed Service Provider (MSP): Services, Benefits, and How to Choose One